E-commerce website development hits a snag, and it is not just about code
E-commerce website development is having a slightly awkward moment in 2026. Not because the tools are getting worse, they are not. But because the modern stack now includes something many teams still treat as an afterthought: automated access controls and anti-bot systems that can block real humans, real buyers, and real freelancers at the worst possible time.
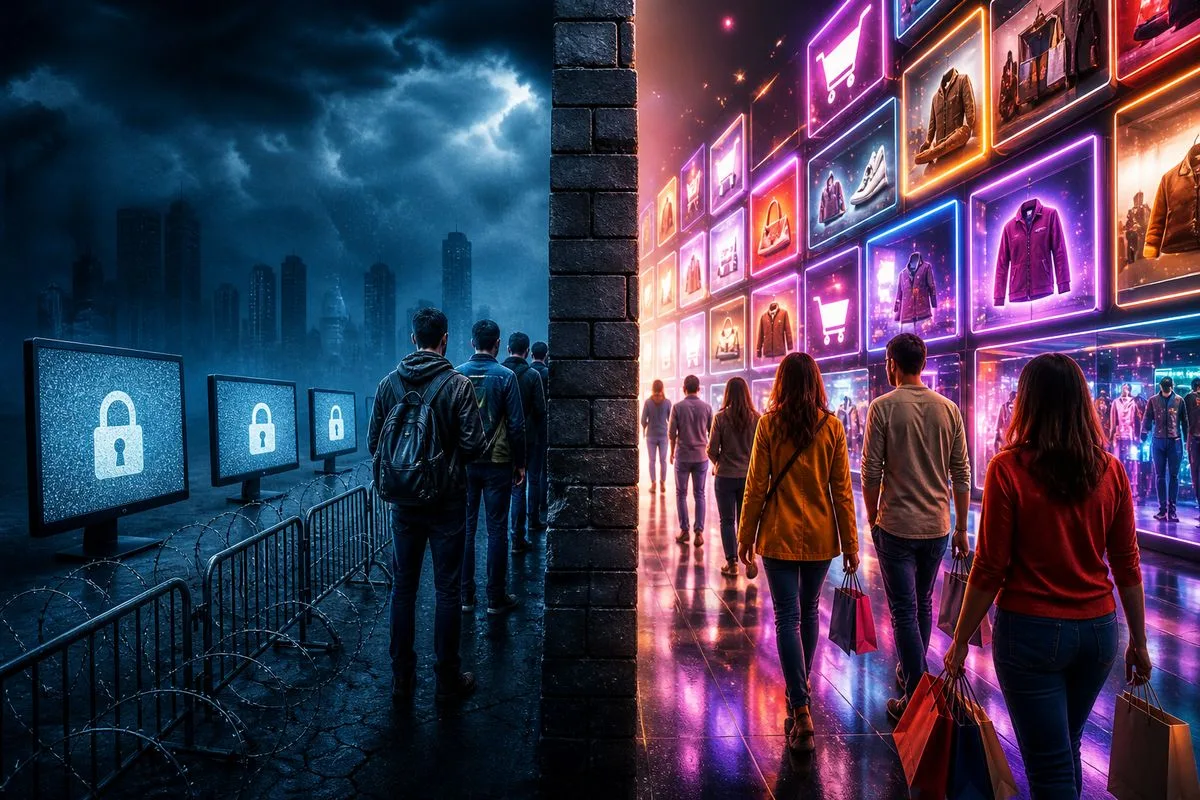
The clearest signal comes from a very practical, very unglamorous incident: a user attempting to access an e-commerce website development services page is met with a “Loading challenge” screen and a set of troubleshooting steps. The message is blunt: disable browser extensions that may interfere, clear cache and cookies, ensure JavaScript is enabled, and update the browser. It also shows an error code, ERRCODE PXCR10002539, plus request details including an IP address 24.199.101.133 and a trace ID 75722ef430384ecd912aa078b2b7120c. That is not marketing copy. That is an operational barrier, in the purchase journey.
And here is the rub. In the same market, platforms are loudly promoting how easy it is to build and optimise online stores, with drag and drop editors, AI creation tools, inventory management, payment processing, shipping automation, and analytics. The promise is speed and simplicity. The reality, increasingly, is that the buyer journey can be interrupted by security friction that sits outside the store owner’s immediate control. It is a big deal, because it changes what “good” looks like in 2026: not just beautiful design, not just conversion rate optimisation, but also reliable access.
The specific 2026 development, access challenges are becoming part of the funnel
The immediate development described in the source material is an access block presented as a “Loading challenge” when attempting to view e-commerce website development services. The instructions are typical of modern bot mitigation flows: disable ad blockers, privacy extensions, or VPNs that may modify web traffic; clear cache and cookies; ensure JavaScript is enabled; update the browser. The presence of a specific error code, PXCR10002539, and a trace ID indicates a structured security system that logs and classifies requests.
What matters is not the identity of the vendor or the user, the material does not provide that. What matters is the pattern: a commercial page that sits near the top of the purchasing funnel is gated by an automated challenge. In plain English, a potential customer is being asked to troubleshoot their browser before they can even browse. Fair enough if the request looks suspicious. But if the system is too aggressive, it can block legitimate traffic, including people researching services, comparing providers, or trying to manage an urgent fix.
This is not an isolated technical footnote. In 2026, the “front door” of e-commerce is no longer just the homepage and product pages. It includes security layers, content delivery networks, anti-fraud tooling, and browser integrity checks. These systems are designed to protect businesses from scraping, credential stuffing, fake checkout attempts, and other abuse. But they also introduce a new conversion risk: friction that is invisible to the store team until someone complains, or until analytics quietly show a drop in sessions that never reach the site.
And that is why this development lands at the intersection of two trends that normally do not share the same meeting room: security engineering and conversion design. The best e-commerce teams now treat access reliability as part of the funnel, because it literally is. If a user cannot load the page, there is no funnel. There is just a dead end.
Background, the platforms shaping e-commerce website development in 2026
On one side of the market are service marketplaces where businesses hire specialists for e-commerce website development, quick fixes, and ongoing optimisation. These marketplaces thrive on speed: a buyer has a problem, they want a solution, and they want it now. That is exactly why access barriers are so damaging. If a buyer hits a challenge screen and cannot proceed, they do not wait politely. They bounce, they search again, they ask a friend, they move on.
On the other side are website building platforms that pitch an end to complexity. The source material describes an e-commerce platform that highlights a drag and drop editor, “online store design features” such as product galleries and interactive shopping features, and AI creation tools that can generate custom images, write product descriptions, and add store sections. It also emphasises operational integrations: online payment processing, shipping automation, inventory management, and multi-channel selling. The message is clear: build quickly, sell smoothly, scale without drama.
There is also a credibility cue: the platform states it is “trusted by over 300M users”. That is the only explicit scale statistic provided in the source material, and it matters because it frames the competitive landscape. When a platform operates at that scale, it sets expectations for what “normal” looks like, including performance, uptime, and the baseline quality of templates and flows. Smaller vendors and bespoke builds are often judged against that standard, even when the underlying constraints are different.
But the most important background point is philosophical, not technical. The design commentary in the source material makes a sharp argument: beautiful and effective are not the same thing. A website is “less of a gallery, more of a salesperson”. The job of the experience is to move a human being from uncertain to certain. That framing is useful because it applies equally to design and to security. A challenge screen, even when justified, creates uncertainty. It asks the user to trust the site enough to change their browser settings. Many will not.
E-commerce website development and the myth of the beautiful store that sells
The design material lays out a scenario that will feel painfully familiar to anyone who has paid for a redesign: months of work, a meaningful chunk of budget, editorial photography, considered typography, a premium colour palette. Friends love it. Investors nod. Then it goes live and conversion barely moves. The point is not that aesthetics do not matter. They do. The point is that aesthetics are not the job. The job is decision-making support.
In 2026, this matters more because the average customer arrives with more questions, not fewer. They are interrogating the page: is the brand real, what do reviews actually say, how much is shipping, what is the return policy, is it buried in the footer. The source material is explicit: every moment a customer cannot find something is a moment where doubt grows and confidence shrinks, and doubt is “conversion poison”. That is strong language, but it is accurate as a description of behaviour.
Now add the access challenge layer on top. A user is already being asked to trust the brand with their money and personal data. If, before they even see the product page, they are asked to disable privacy extensions or a VPN, the trust hurdle gets higher. Not everyone uses those tools for shady reasons. Some use them for basic privacy hygiene, or because their employer mandates it. So the store experience has to do more work, earlier, to reassure the visitor.
This is where e-commerce website development becomes less about building pages and more about orchestrating an end to end journey, including the bits that feel “outside” the website. The funnel is not just arrival, evaluation, checkout. It is also access, performance, and the ability to load reliably across devices, networks, and browser configurations. Not exactly groundbreaking as a concept, but many teams still behave as if it is optional.
Industry implications, security friction is now a conversion variable
The industry implication is straightforward: anti-bot and anti-fraud systems are no longer purely defensive infrastructure. They are part of the customer experience, whether anyone likes it or not. The “Loading challenge” flow described in the source material is a customer-facing interface. It gives instructions, it sets expectations, and it can stop a purchase journey cold. That makes it a conversion variable, and therefore a commercial variable.
For service marketplaces and SaaS platforms, the risk is compounded because the blocked page is often a high-intent page. Someone looking for e-commerce website development services is not casually browsing. They are likely trying to solve a problem, perhaps urgently. If the system blocks them, the platform does not just lose a page view. It potentially loses a transaction, a repeat customer, and the network effects that come from satisfied buyers and sellers.
For merchants building their own stores, the lesson is similar but the control surface is different. Many merchants rely on third-party scripts for payments, reviews, personalisation, analytics, and marketing. Each script can affect performance and can trigger security heuristics in unexpected ways. Meanwhile, the platform marketing emphasises ease: drag and drop, AI generation, seamless integrations. The danger is that “easy to add” becomes “hard to govern”. When something breaks, it breaks in the customer’s browser, not in the merchant’s dashboard.
And there is a deeper strategic implication. As platforms compete on AI features and design flexibility, the baseline experience converges. Templates get better. Product galleries get slicker. Copy generation becomes table stakes. So differentiation shifts to reliability, trust signals, and operational excellence. In that world, a single overzealous security rule can do more damage than a mediocre hero image. It is not glamorous, but it is where money is won and lost.
Historical context, from simple storefronts to layered, automated gatekeepers
Early e-commerce was comparatively simple: a storefront, a catalogue, a checkout, and a payment gateway. Security existed, of course, but it was often invisible until something went wrong. Over time, as fraud, scraping, and automated abuse increased, the industry layered on defences. First came more robust payment verification and fraud scoring. Then came bot detection, rate limiting, and content delivery networks. Now, in 2026, many sites effectively run a pre-flight check on the visitor’s browser before granting access.
This evolution mirrors what happened in other consumer internet sectors. Media sites introduced paywalls and ad-block detection. Ticketing sites introduced queues and identity checks. Financial services introduced step-up authentication and device fingerprinting. E-commerce is following the same path, because the incentives are the same: protect revenue, protect inventory, protect customer accounts, and reduce operational costs from abuse.
But e-commerce has a unique sensitivity: conversion is fragile. The design commentary in the source material captures the psychology well. The customer is not admiring the layout, they are interrogating. They are looking for answers in a specific order. Anything that interrupts that sequence, whether it is a missing size guide or a security challenge, introduces doubt. And doubt is the enemy.
So the historical comparison is not “security versus design”. It is “layers versus flow”. The more layers the industry adds, the more disciplined teams must be about keeping the flow intact. That discipline is now a core competency in e-commerce website development, right alongside design systems, performance optimisation, and analytics.
What This Means For You
For readers responsible for an online store, or for commissioning e-commerce website development in 2026, the practical takeaway is simple: treat access and trust as first-class product features. If a user hits a challenge screen, they are being asked to do work. Some will. Many will not. So it is worth auditing where and how security challenges appear, and whether they disproportionately affect high-intent pages. If the only time the team hears about it is when a customer complains, that is already too late.
For teams focused on design and conversion, the message is slightly uncomfortable but useful. A beautiful redesign that does not answer customer questions is wasted effort. The source material’s framing is the right one: the website is a salesperson, and every element should move a person from uncertain to certain. That means making shipping costs, delivery estimates, returns policies, contact options, and reviews easy to find, not hidden. It also means recognising that security friction creates its own questions: why is this site blocking access, is it safe, is it worth the hassle. The store experience should anticipate that and reduce anxiety wherever possible.
And for freelancers and agencies selling e-commerce website development services, this is an opportunity as much as a headache. Clients increasingly need help not just building pages, but diagnosing why traffic does not convert, why users cannot access the site, or why certain browser setups fail. The “quick fixes” mindset in the source material is telling. The market values speed. So the winning providers will be the ones who can combine UX thinking, technical troubleshooting, and a pragmatic approach to security and performance, without turning every issue into a six-week project.
Closing thoughts, the next competitive edge is boring, and that is the point
The story here is not that e-commerce platforms are failing. If anything, they are getting more capable, more accessible, and more automated. Drag and drop building, AI-assisted content creation, and integrated operations are real advantages, and the scale claim of over 300M users underscores how mainstream these tools have become. But capability does not automatically translate into smooth customer journeys. The gap between “can be built” and “can be trusted” is where many stores stumble.
The access challenge incident, complete with error code PXCR10002539 and trace ID 75722ef430384ecd912aa078b2b7120c, is a reminder that the modern storefront has gatekeepers. Some are necessary. Some are misconfigured. Either way, they shape revenue. And they shape perception. A customer who cannot load a page does not think, “ah, sophisticated bot mitigation”. They think, “this site is broken”, and they leave.
In 2026, the competitive edge in e-commerce website development is increasingly the boring stuff done well: reliable access, clear answers, fast pages, and a funnel that respects how humans make decisions. The brands that win are not necessarily the ones with the prettiest sites. They are the ones that remove doubt, step by step, including the doubt created by the very systems meant to protect them.